Videos & Demos
1 VideoOfficial technical walkthroughs and demonstrations verified directly from the vendor.
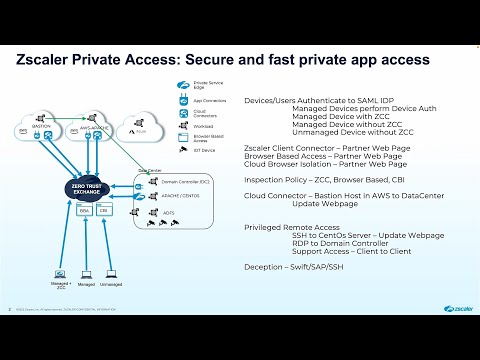
Zscaler Private Access (ZPA) Platform Demo
Factual Product Summary
Zscaler Private Access from Zscaler focuses on zero trust access to private applications. It is secure access and networking technology used for applying access policy to users, applications or traffic. Capabilities - Application-specific private access: Connects users to private applications using the documented zero trust access model. - Zero trust network access: Grants access to the applications or resources defined by policy rather than relying solely on network location. - Private application access: Connects authorized users to private applications according to access policy. - Remote workforce access: Addresses secure connectivity for users working beyond a traditional office network. Use and operational context Zscaler Private Access is relevant to teams supporting distributed users and application access when the requirement centers on applying access policy to users, applications or traffic. Scope the evaluation around the functions listed above and the assets or workflows that need coverage. A useful trial should use representative business conditions so the team can assess the quality of the results and the effort needed to act on them. Deployment and evaluation Deployment: Cloud service / SaaS. Before adoption, review identity integration, application reachability, traffic routing and the user experience during a staged rollout. Assign an owner for administration, document required permissions and identify how the product or service will fit the existing operating process. Buyer questions - What is the main purpose? Zscaler Private Access focuses on applying access policy to users, applications or traffic. - What should a proof of concept establish? Test the listed capabilities against representative assets and workflows, record useful results and unresolved gaps, and confirm who handles follow-up work. - What should be confirmed before purchase? Ask the vendor which edition or service scope includes the required features, which dependencies must be configured and what licensing or contract terms apply. Pricing has not been verified for this catalog.
Documented Technical Capabilities
Core enterprise capabilities verified directly from official vendor engineering documentation.
Audited Ecosystem & Architecture Integrations
Native connectors, SIEM/SOAR forwarders, cloud APIs, and identity providers confirmed for interoperability.
Eliminates traditional legacy VPN concentrators by establishing outbound-only App Connector tunnels.
Documented Capabilities & Sourced Claims
Every claim is checked against official engineering documentation or compliance reports.
Makes internal applications invisible to the public internet using inside-out connection tunnels
Audited Capability Specifications
Structured criteria validated against official vendor documentation for buyer comparison.
Architectural delivery model (Unified SASE, Cloud-Delivered SSE, Hybrid Mesh NGFW).
Published edge data center points of presence providing direct peering and low latency.
Application-level micro-segmentation without placing users on the corporate network.
In-line deep packet inspection, TLS decryption, and zero-day sandboxing.
Official Sources & References
Deployment & Specifications
- Deployment Models
- Cloud service / SaaS
- Supported Platforms
- Not documented in our sources
- Customer Segments
- Enterprise
- Service Geography
- Global
Pricing Transparency
About the Vendor
Zscaler offers a portfolio covering adding expert monitoring and response to supported telemetry and applying access policy to users, applications or traffic. The entries in this catalog include Red Canary Managed Detection and Response, Zscaler Digital Experience, Zscaler Internet Access and Zscaler Private Access. Red Canary Managed Detection and Response focuses on managed threat detection and response across security telemetry. Zscaler Digital Experience focuses on user experience monitoring and connectivity diagnostics. Zscaler Internet Access focuses on secure internet access and cloud-delivered inspection. When reviewing Zscaler, compare the named products individually: a platform family, a specific module and a managed service can have different scopes and purchasing requirements. Selection should account for supported data sources, response authority, escalation responsibilities and the actions included in the service agreement. Portfolio detail - Red Canary Managed Detection and Response: the catalog lists Managed threat monitoring, Human-led investigation, Threat hunting services. - Zscaler Digital Experience: the catalog lists Application experience diagnostics, Zero trust network access, Data loss prevention controls. - Zscaler Internet Access: the catalog lists Internet-bound access security, Zero trust network access, Secure web gateway. - Zscaler Private Access: the catalog lists Application-specific private access, Zero trust network access, Private application access. For procurement, map each required capability to a named offering and confirm the edition, dependencies and delivery responsibility with the vendor. Product-level entries below provide the operational context and evaluation questions for that comparison.